Microsoft and Over 40 Organizations Launch AI Transparency Initiative
en.Wedoany.com Reported - On November 17, Microsoft launched the "AI Transparency Initiative" at the Ignite 2026 conference held in San Francisco, joining forces with more than 40 organizations including Accenture, Adobe, KPMG, Mastercard, and Volvo Cars to develop open standards for transparency, security, and governance applicable to different AI models and providers. Microsoft plans to expand its collaboration with the U.S. National Institute of Standards and Technology (NIST) and incorporate the relevant technical outcomes into its AI products and services.
Microsoft will further participate in the NIST agent standards initiative, leveraging relevant research to advance industry standards for AI transparency, security, and governance requirements. Partner organizations will jointly research mechanisms for AI system behavior logging, independent verification, and permission control. The standards cover both closed-source models and open-weight models, and apply to products offered by different model providers.
The relevant standards will be progressively integrated into Microsoft AI, Microsoft Foundry, and Microsoft Copilot products and services. Enterprise customers can obtain behavioral evidence of AI models and agents through Microsoft or third-party security and compliance tools, and conduct independent security reviews and compliance verification.
The technical mechanisms proposed by Microsoft comprise three parts: AI behavior observability, verifiability, and controllability. Behavior logging will cover the tasks received by agents, the models and runtime environments used, the data and tools accessed, the operations performed, and related permissions and risk signals. The verification mechanism will distinguish between behavior logs generated by the models themselves and independent evidence formed by runtime environments, identity management, and policy systems, enabling enterprises to verify the actual operations of agents.
The permission control mechanism will record the task purpose, responsible parties, data usage scope, and authorized permissions of AI workflows, enabling enterprises to enforce security policies before critical operations are executed, and to trace agent operation records during security investigations, incident response, and audits. The relevant behavioral evidence can continue to be used for security management and compliance reviews even after enterprises switch models or providers.
Related Products

Flat Portable Satellite Terminal 0.35m Aperture Manual Portable Terminal
China Starwin Science & Technology Co., Ltd.
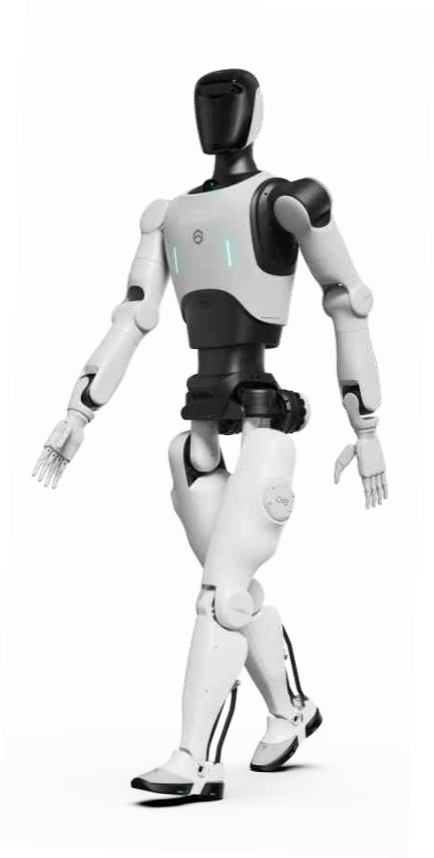
D12 Humanoid Robot
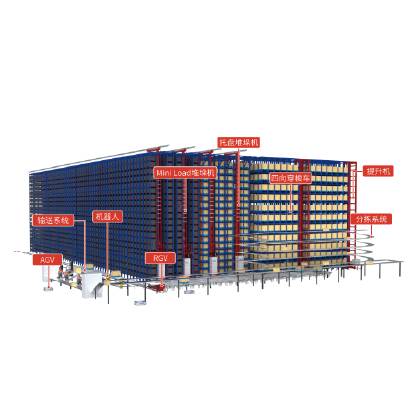
Automation Research Institute Co., Ltd. of China South Industries Group Corporation
G.652.D Wavelength-extended Non-dispersion Shifted Single-mode Optical Fiber
HONGAN GROUP CO., LTD.
TWP16 P-Band Tropospheric Wind Profile Radar
China Huayun Meteorological Technology Group Co., Ltd.